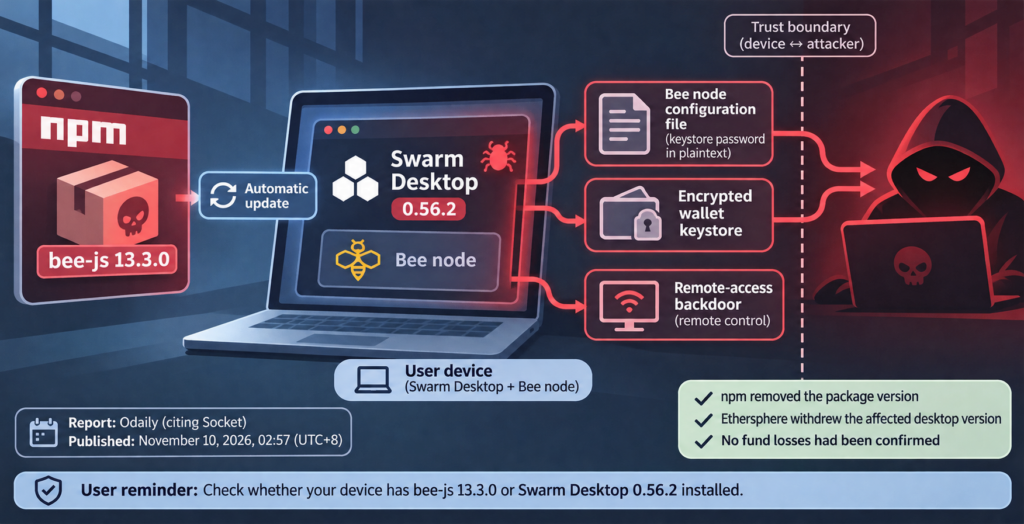
If you use Swarm Desktop, the version installed on your device matters for wallet security. In a report published on November 10, 2026, at 02:57 (UTC+8), Odaily cited Socket’s monitoring of a supply-chain attack affecting Swarm developer Ethersphere.
According to Socket, an attacker published a malicious bee-js version, 13.3.0, to npm on November 9. A trojanized Swarm Desktop 0.56.2 was then distributed through automatic updates. Socket reported that the malicious code read Bee node configuration files and encrypted wallet keystores and sent them to the attacker. Because the configuration file stored the keystore password in plaintext, node wallets may have been exposed. The code also installed a remote-control backdoor on affected devices.
At the time of the report, npm had removed the package version and Ethersphere had withdrawn the affected desktop version. No fund losses had been confirmed. Users can check whether they installed either affected version; the report does not establish that every Swarm wallet was compromised.
Source: odaily.news (originally published 2026-11-10 02:57 UTC+8)