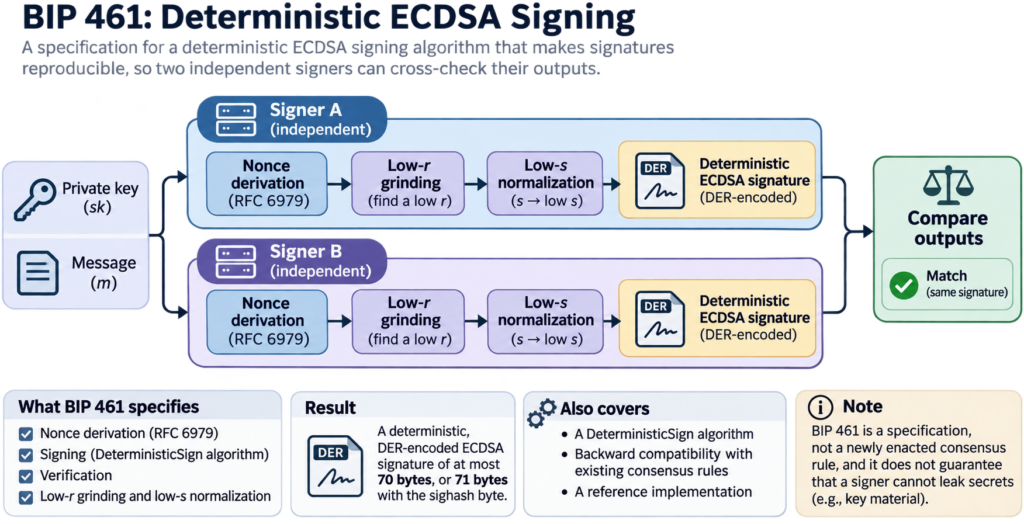
For someone relying on a wallet signer, a key question is whether two independent signers produce the same signature for the same private key and message. In a description published on November 18, 2026, BIP 461 sets out a deterministic ECDSA signing algorithm intended to make that comparison possible.
The specification derives the nonce using RFC 6979, applies low-r grinding and normalizes s to its low value. Under this algorithm, the private key and message determine the signature rather than leaving the signer free to choose the nonce or s. The resulting DER-encoded signature is at most 70 bytes, or 71 bytes with the sighash byte.
That consistency would let two independent signers cross-check their outputs for signs that key material might be leaking. The description also covers nonce derivation, signing, verification and a DeterministicSign algorithm, and discusses backward compatibility with existing consensus rules and a reference implementation. It describes a specification, not a newly enacted consensus rule or a guarantee that a signer cannot leak secrets.