For anyone holding a pool token, the underlying question is whether it can be redeemed against the assets in the pool as expected. In an analysis published on December 4, 2025, SlowMist described how an attacker exploited calculations in Yearn’s yETH Weighted Stableswap Pool to mint more yETH LP tokens than intended. SlowMist’s MistTrack estimated the attacker’s profit at about $9 million.
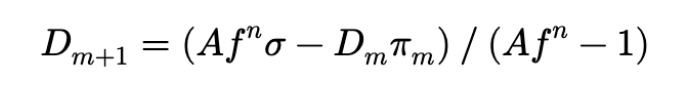
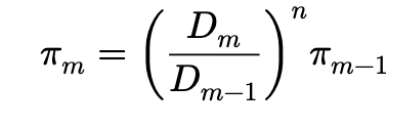
Where the calculation failed
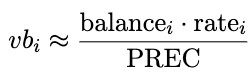
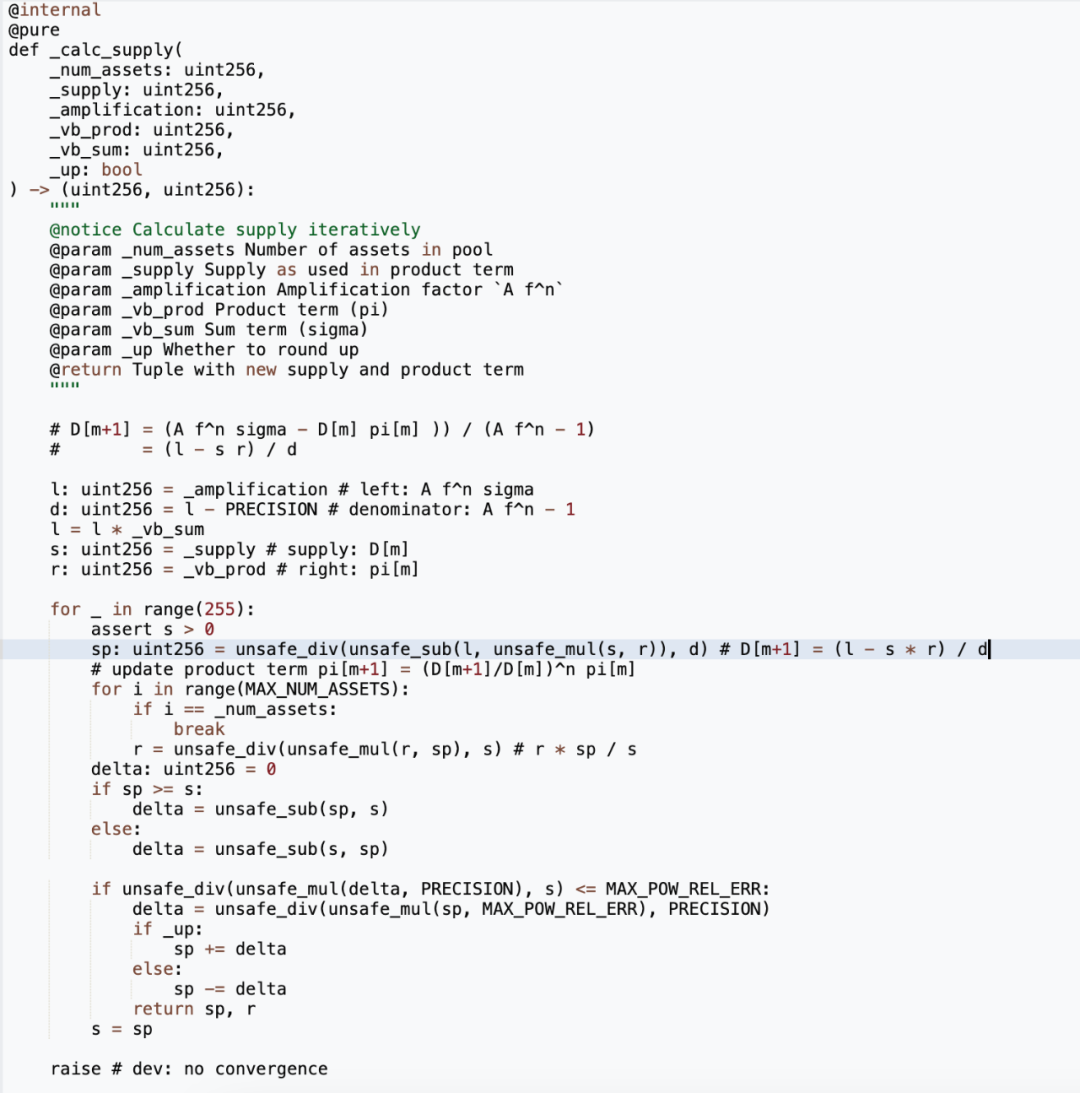
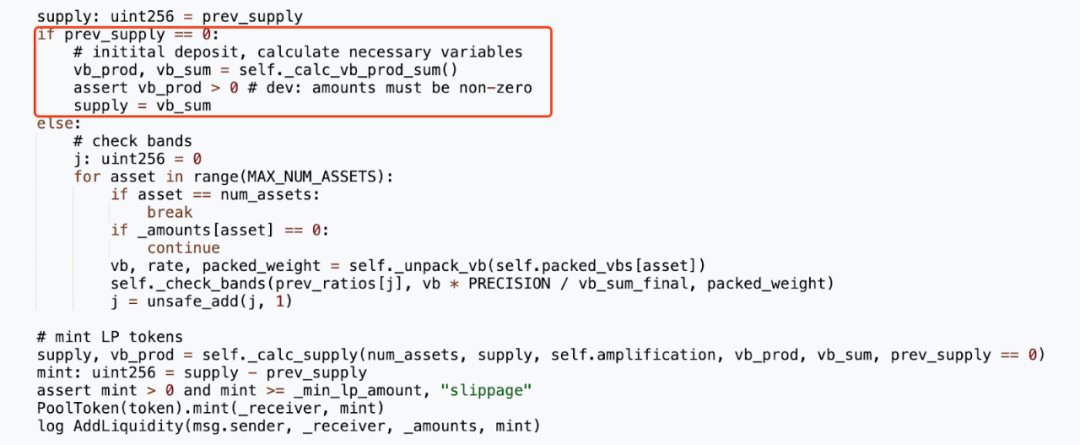
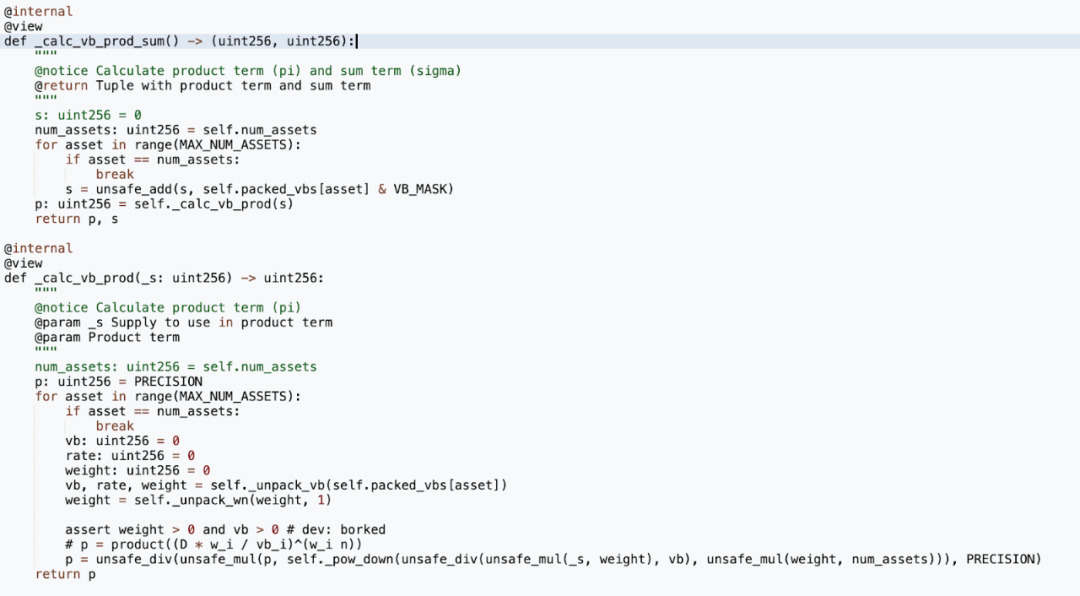
The pool held eight liquid-staking assets and tracked their rate-adjusted virtual balances, their sum (vb_sum), their product (vb_prod), and an LP supply value called D. According to SlowMist, the pool’s _calc_supply function used unchecked arithmetic and rounding in calculations that updated these values.
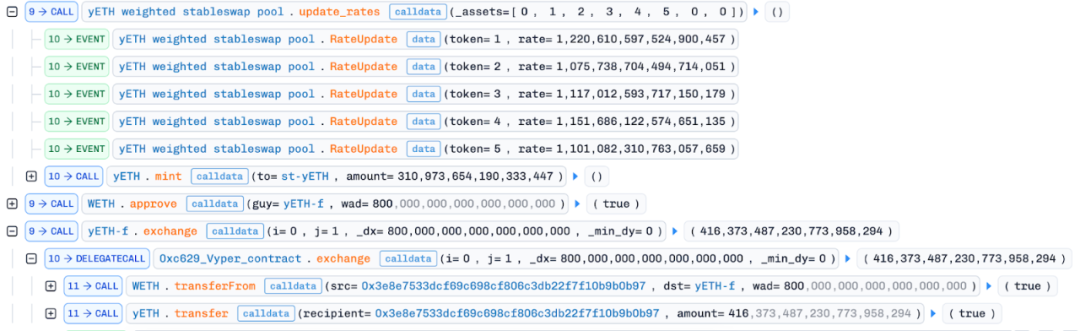
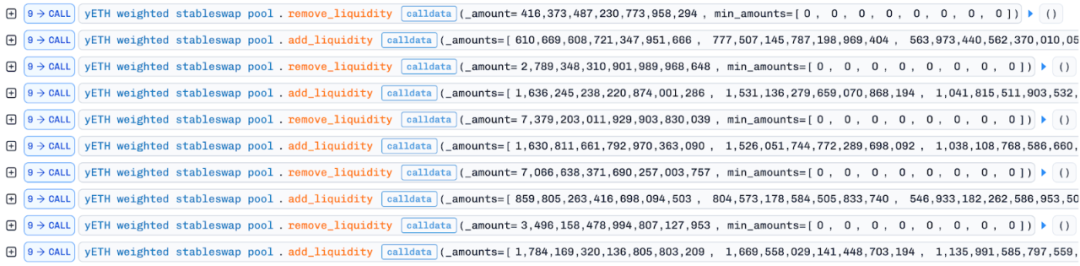
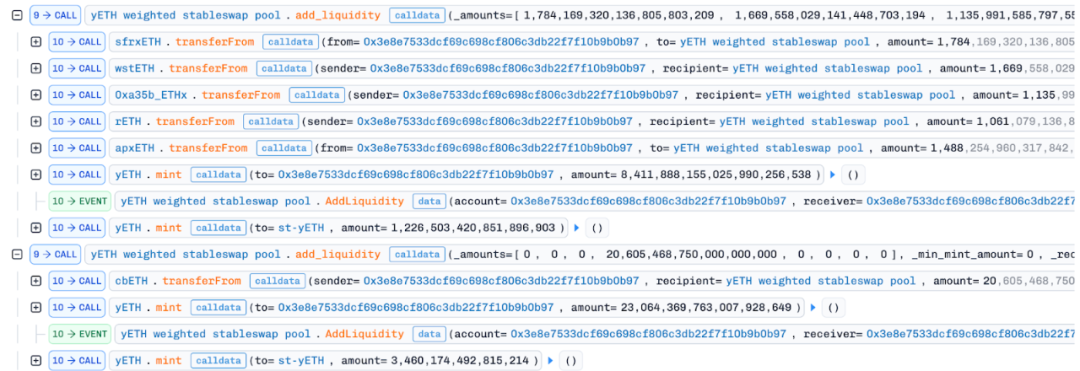
SlowMist’s reconstruction says the attacker repeatedly removed liquidity and added back only selected assets. On the fifth addition, a subtraction underflow produced an unexpectedly small intermediate supply value. The next product calculation rounded vb_prod down to zero. Later iterations then calculated an inflated supply value, allowing the attacker to mint excess yETH. A further single-asset deposit minted additional yETH under the manipulated state.
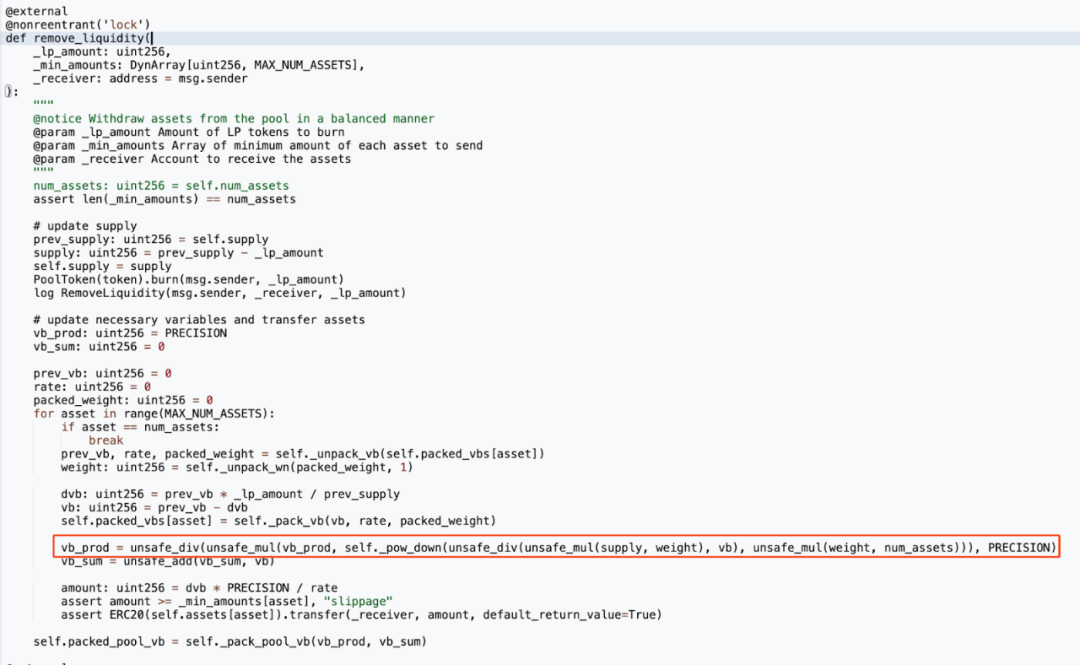
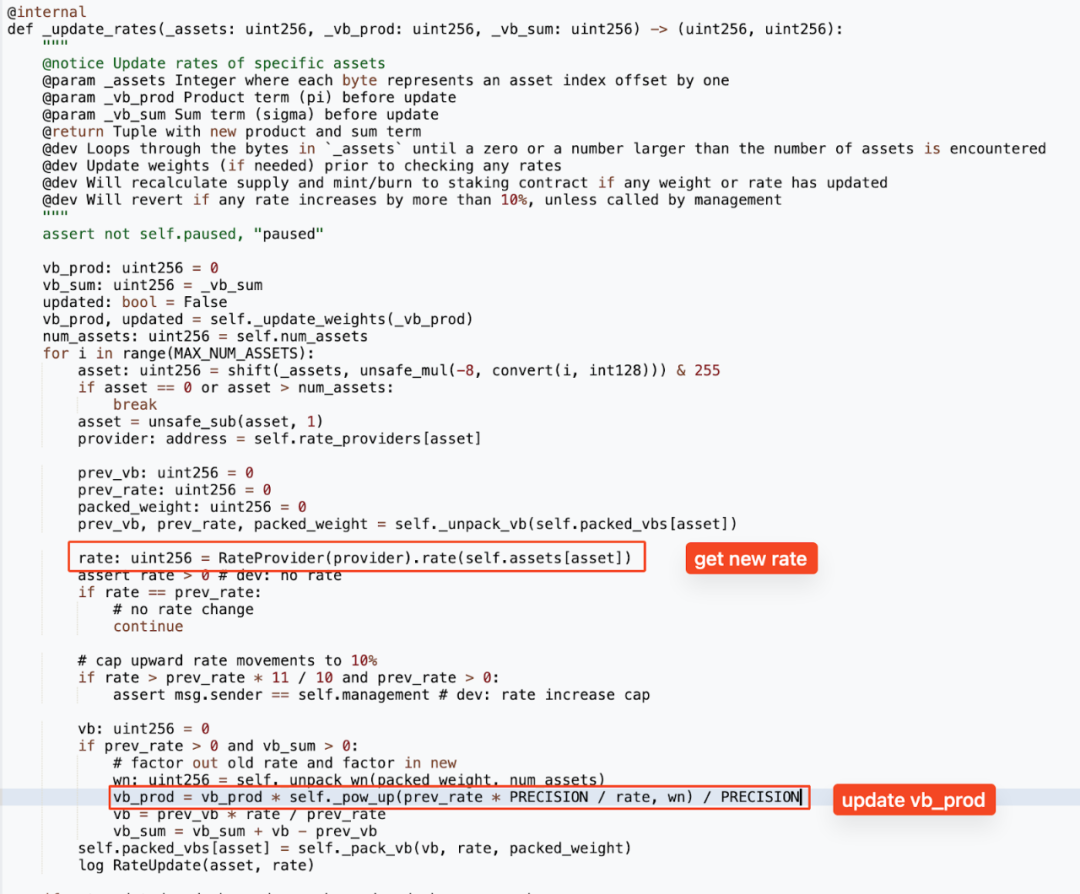
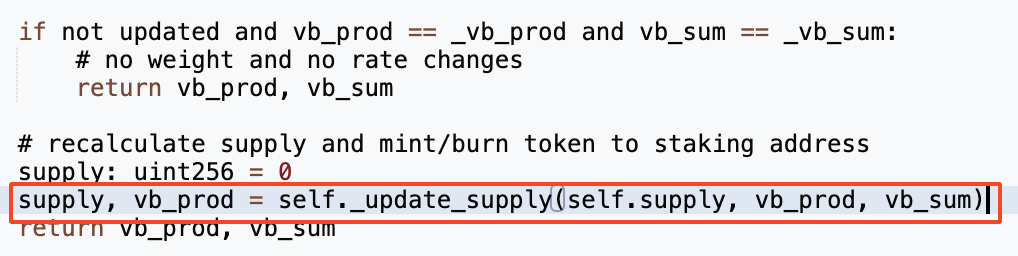
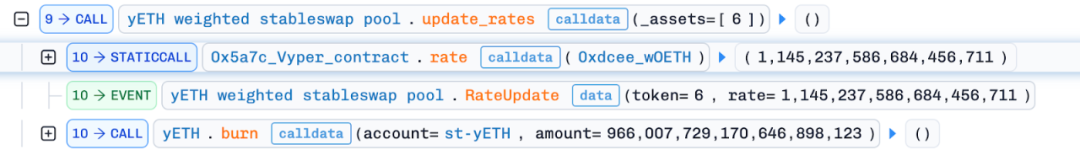
The attacker subsequently called remove_liquidity with zero LP tokens. SlowMist said this recalculated vb_prod to a nonzero value without changing the pool’s balances. An update to the wOETH exchange rate then reduced the calculated supply. The attacker redeemed LP tokens minted under the earlier, inflated calculation after that change. SlowMist says repeated use of this sequence eventually emptied the pool.
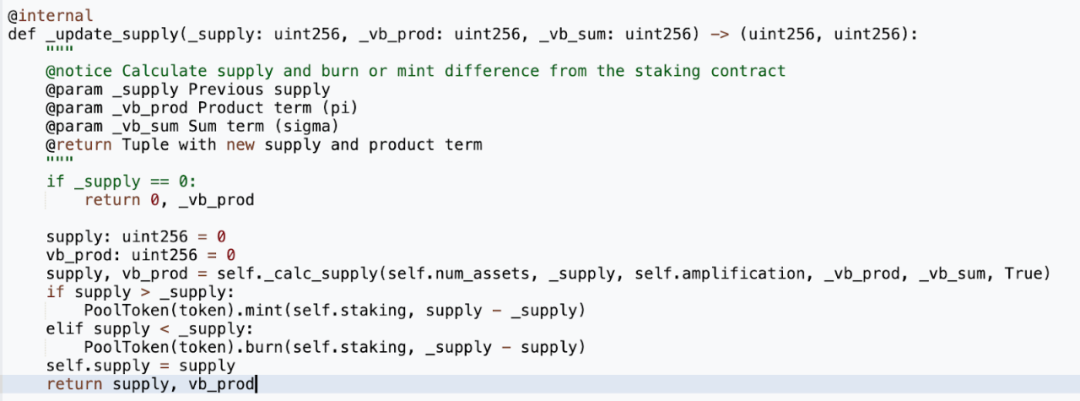
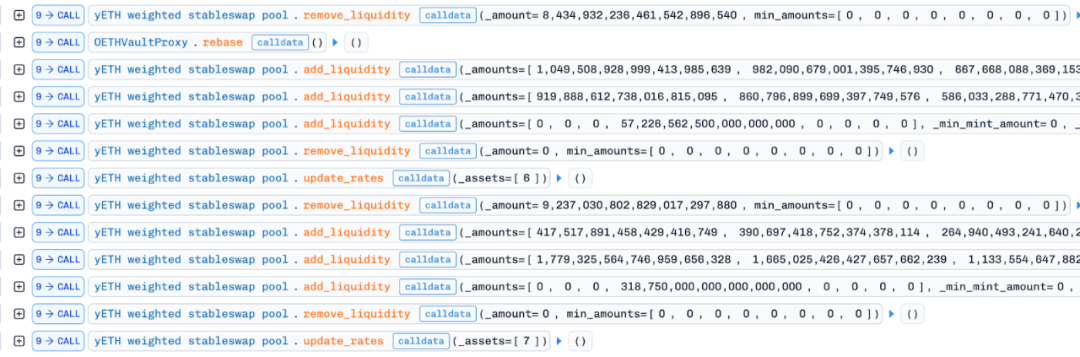
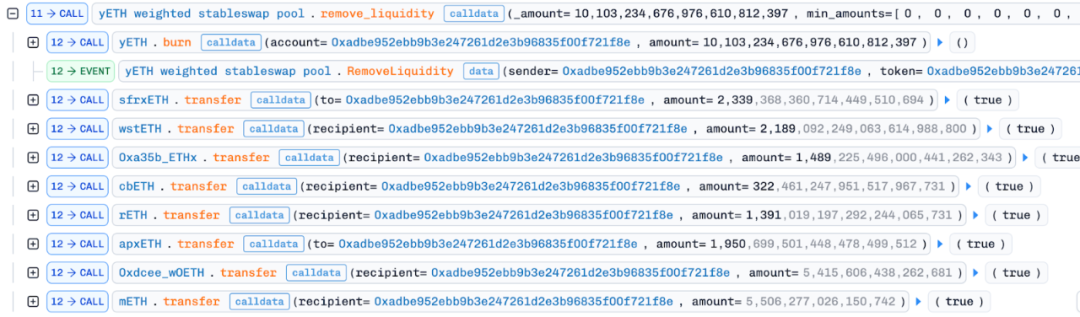
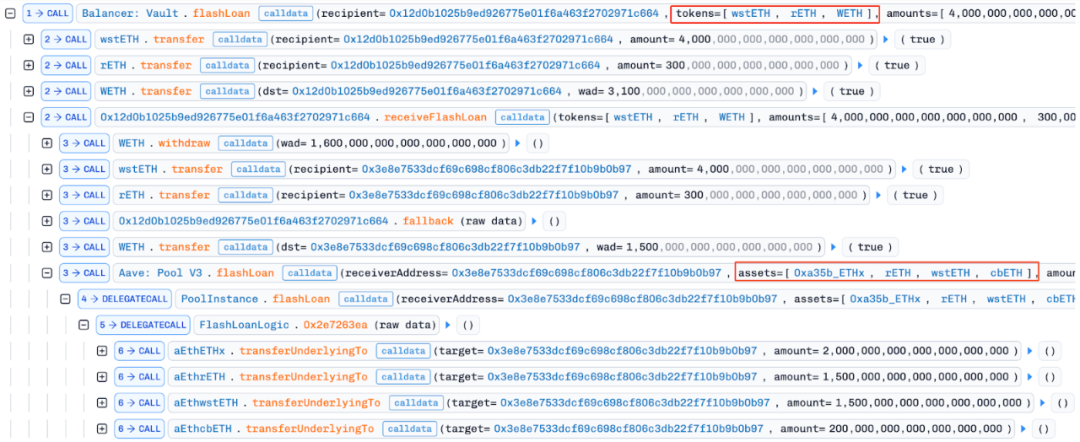
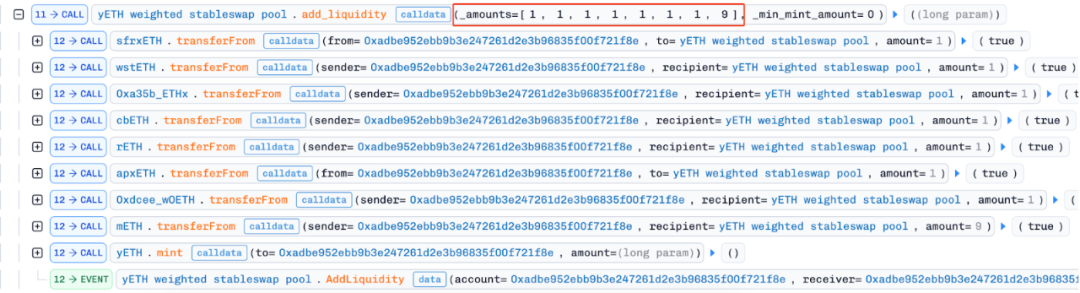
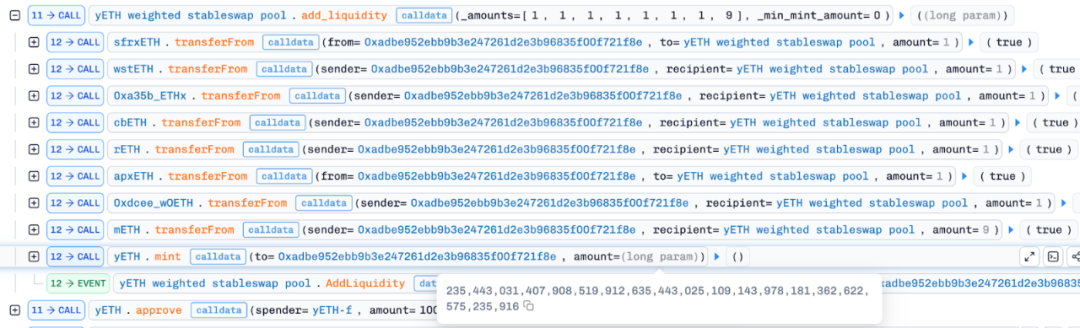
With the pool empty, the attacker added tiny amounts of assets. SlowMist found that an unchecked multiplication in another _calc_supply iteration overflowed, producing a calculated supply of approximately 2.354 × 10⁵⁶ and minting a corresponding amount of yETH. The attacker then sold yETH through an AMM and repaid flash loans, according to the analysis.
Funds traced and the defensive lesson
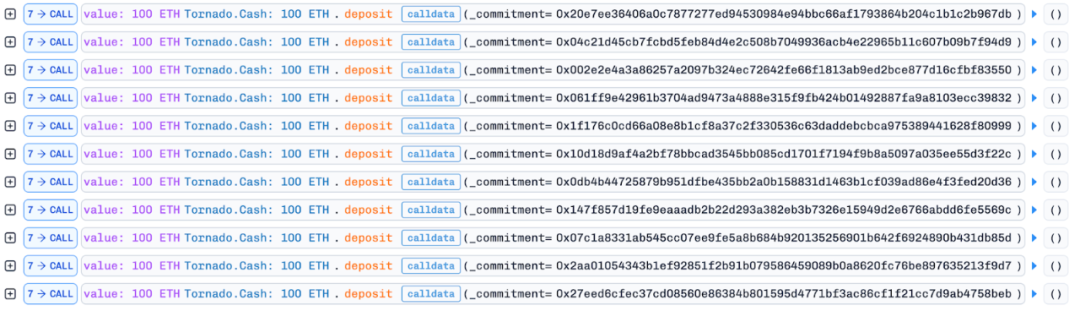
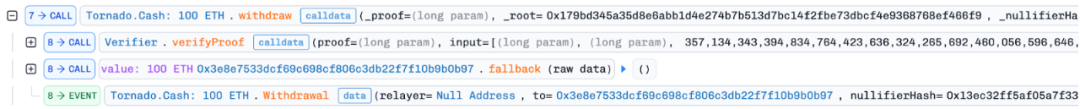
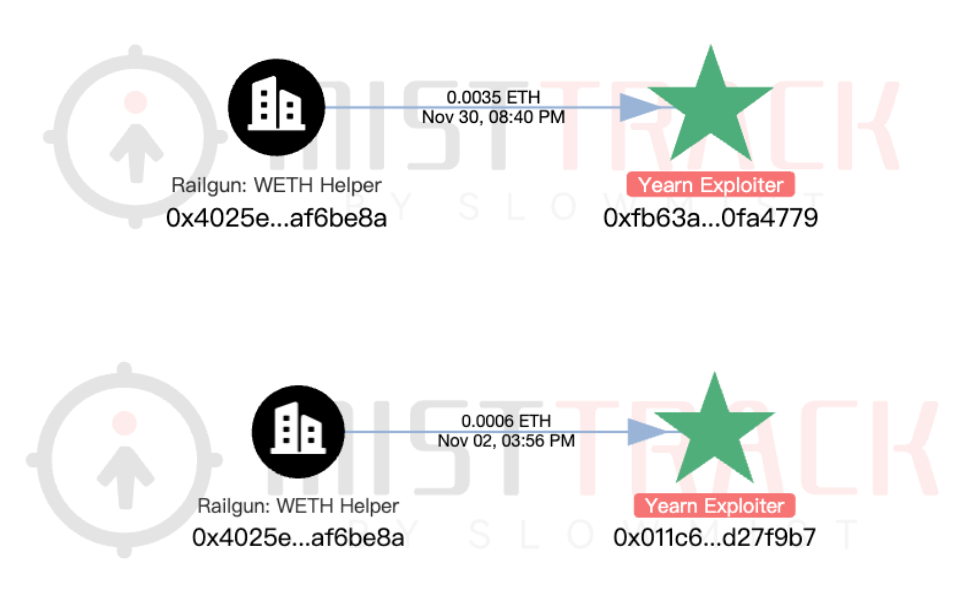
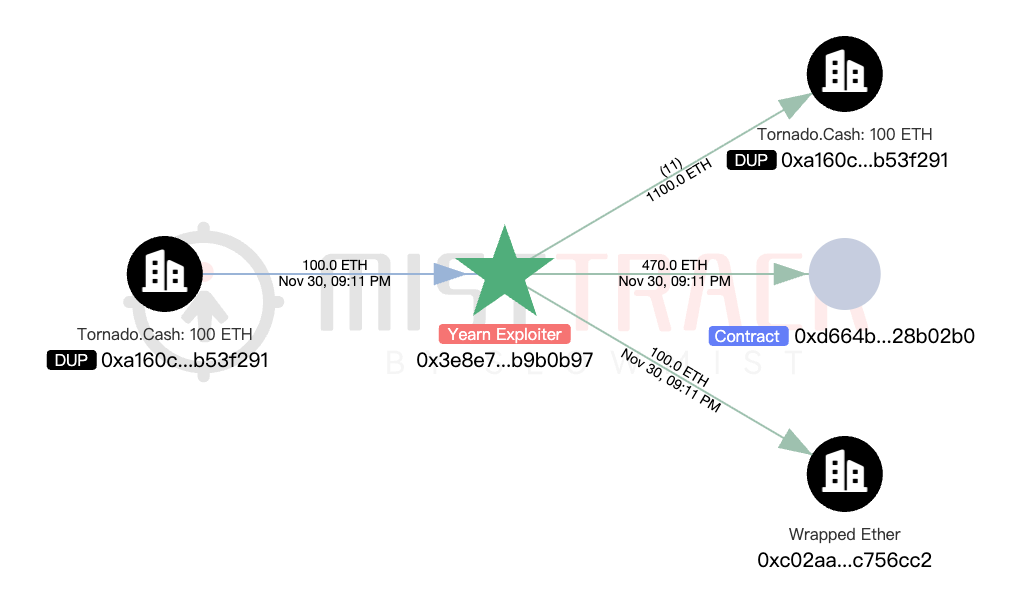
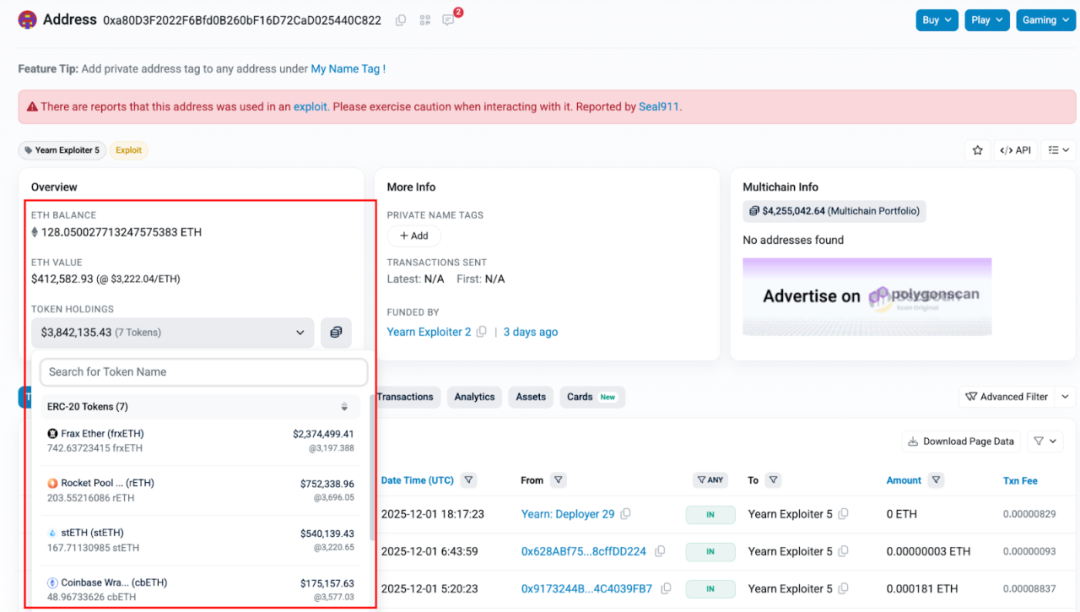
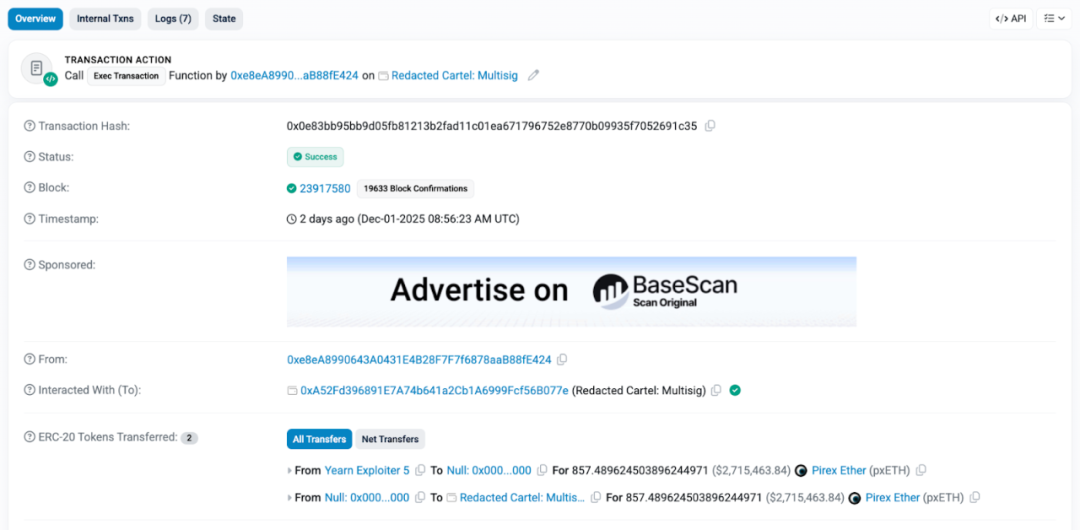
MistTrack reported that the attack began with a small amount of ETH transferred from Railgun. It said the attacker sent 1,100 ETH to Tornado Cash after the attack and withdrew 100 ETH for further exploitation; it also traced approximately $6 million in remaining proceeds to a single address. SlowMist reported that Yearn later recovered $2.4 million by burning pxETH held by the attacker, with 857.48 pxETH reminted and returned to a Redacted Cartel multisignature wallet.
This was a pool-accounting exploit, not a reported compromise of holders’ wallet keys. SlowMist’s recommendation for projects and auditors was to test extreme states and boundary conditions and to check arithmetic used for core accounting values, particularly where overflow or rounding can affect LP supply.