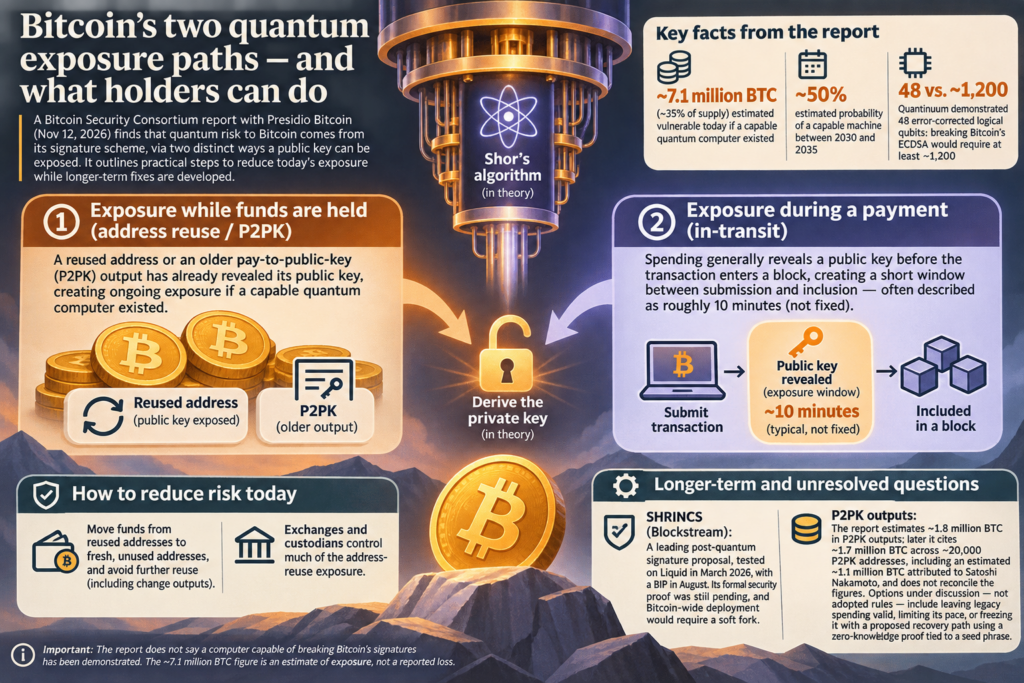
If you hold bitcoin for the long term, the immediate custody question is whether an address has been reused. A Bitcoin Security Consortium report, prepared with Presidio Bitcoin and published on November 12, 2026, identifies address reuse as a source of quantum exposure that holders can reduce today. It does not say a computer capable of breaking Bitcoin’s signatures has been demonstrated.
Two ways a quantum attack could work
The report focuses on Bitcoin’s signature scheme, not its supply cap, issuance schedule or transaction-consensus rules. A sufficiently capable quantum computer running Shor’s algorithm could, in theory, derive a private key from an exposed public key. It describes two distinct risks:
- Exposure while funds are held: Reused addresses and older pay-to-public-key (P2PK) outputs have already revealed their public keys. Project Eleven estimates that roughly 7.1 million BTC, or about 35% of the total supply, would be vulnerable to theft if a capable quantum computer existed today. The report says about three-quarters of that amount is in reused addresses, many associated with large exchanges. This is an estimate of exposure, not a reported loss.
- Exposure during a payment: Spending generally reveals a public key before the transaction enters a block. The relevant window is the time between submission and inclusion—often described as roughly 10 minutes, though it is not fixed. Google estimates that a hypothetical, prepared fast-clock quantum device could complete the key-derivation calculation in as little as nine minutes. That is a theoretical estimate, not an observed Bitcoin attack.
The report says most bitcoin held in modern output types is not exposed to the first kind of attack before spending because the public key remains hidden. That distinction does not eliminate the second risk.
Progress is not a working attack
The consortium points to advances in error correction and proposed optimizations of Shor’s algorithm, including work reported in 2026 by Google Quantum AI, Oratomic/Caltech, ECDSA.fail and IonQ. It distinguishes those results and blueprints from a machine that can break Bitcoin’s cryptography. According to the report, the demonstrated Quantinuum system had 48 error-corrected logical qubits, while breaking Bitcoin’s elliptic-curve cryptography would require at least approximately 1,200. Scaling up reliable operations remains an engineering challenge.
The report also cites a recent expert survey assigning roughly a 50% probability to a capable machine emerging between 2030 and 2035. That is a forecast, not a deadline or a confirmed capability.
What holders can do, and what remains unresolved
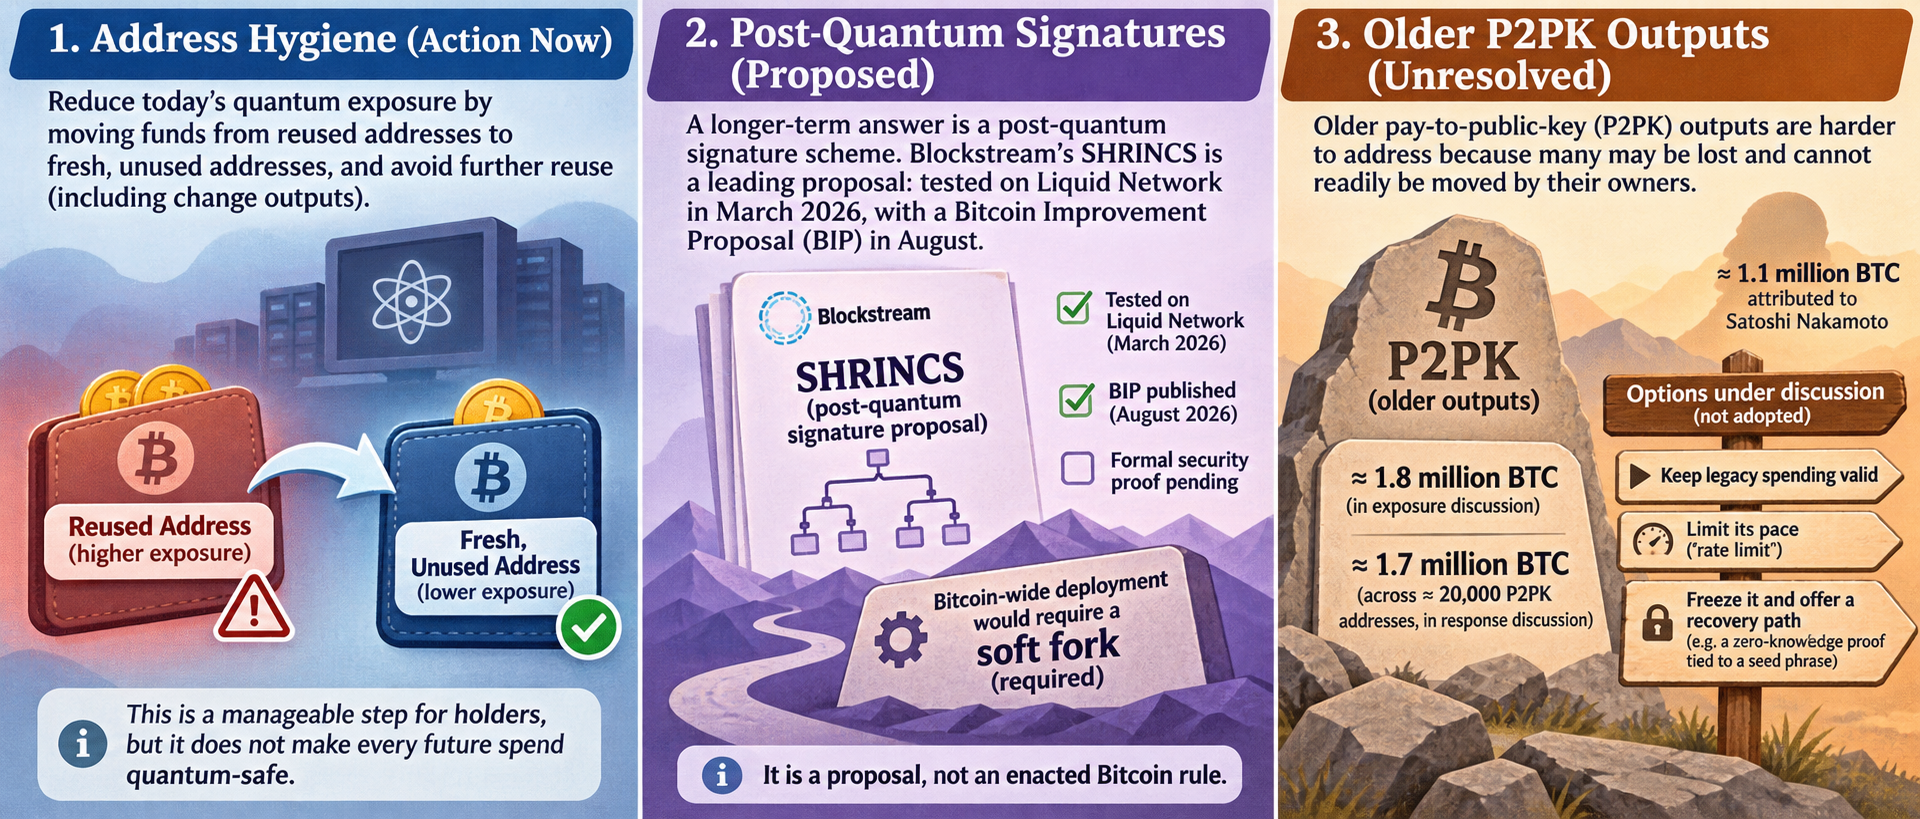
For funds in reused addresses, the report’s practical measure is to move them to fresh, unused addresses and avoid further reuse, including when handling change outputs. Exchanges and other custodians control much of this address-reuse exposure; a self-custody holder can review their own address practices. Moving funds does not make every stage of a future spend quantum-safe.
A longer-term answer requires a post-quantum signature scheme. The report identifies Blockstream’s SHRINCS as a leading proposal: Blockstream tested it on Liquid Network in March 2026, and a Bitcoin Improvement Proposal followed in August. Its formal security proof was still pending, and Bitcoin-wide deployment would require a soft fork. It was not an enacted Bitcoin rule at the time of the report.
Older P2PK outputs pose a harder question because many may be lost and therefore cannot readily be moved by their owners. The report gives an estimate of 1.8 million BTC in P2PK outputs in its discussion of exposure; later, in discussing possible responses, it cites about 1.7 million BTC across roughly 20,000 P2PK addresses, including an estimated 1.1 million BTC attributed to Satoshi Nakamoto. It does not reconcile those figures. Presidio Bitcoin describes options under discussion—not adopted rules—including leaving legacy spending valid, limiting its pace, or freezing it while offering owners a proposed recovery path using a zero-knowledge proof tied to a seed phrase.
The manageable step for holders is to check for address reuse without mistaking that precaution for a complete solution. The report’s remaining questions depend on cryptographic development and Bitcoin consensus, not on a custody setting any individual can change alone.