If you use a Gnosis Pay card, the immediate concern is exposure of payment and personal information—not a reported loss of funds. In a report published on Nov. 7, 2026, at 04:51 (+08:00), Cointelegraph said Gnosis Pay had disclosed unauthorized access to its legacy consumer card system. The company said it detected the access on Nov. 3 and began containing the breach within two hours.
According to breach notifications reviewed by Cointelegraph, exposed information included full card numbers, expiration dates, CVV codes, names, home addresses and cryptocurrency wallet addresses linked to affected accounts. Email addresses, phone numbers and nationalities were also exposed; some records included banking details such as IBAN and BIC information. Gnosis Pay did not disclose how many customers were affected.
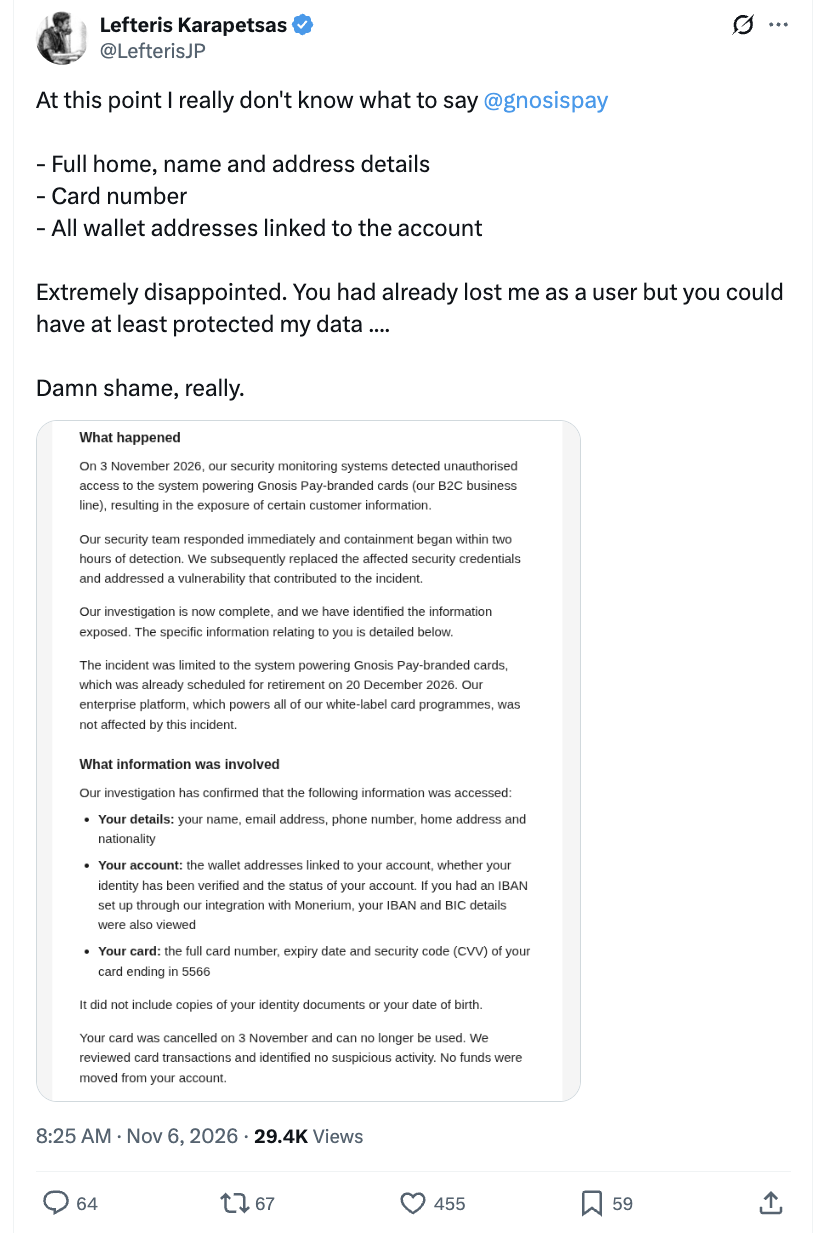
Gnosis Pay said customer funds and its separate enterprise platform were unaffected. One notification reviewed by Cointelegraph said that customer’s card was canceled on Nov. 3 and that no suspicious transactions or movement of funds had been detected for that customer. That notification does not establish the status of every affected account.
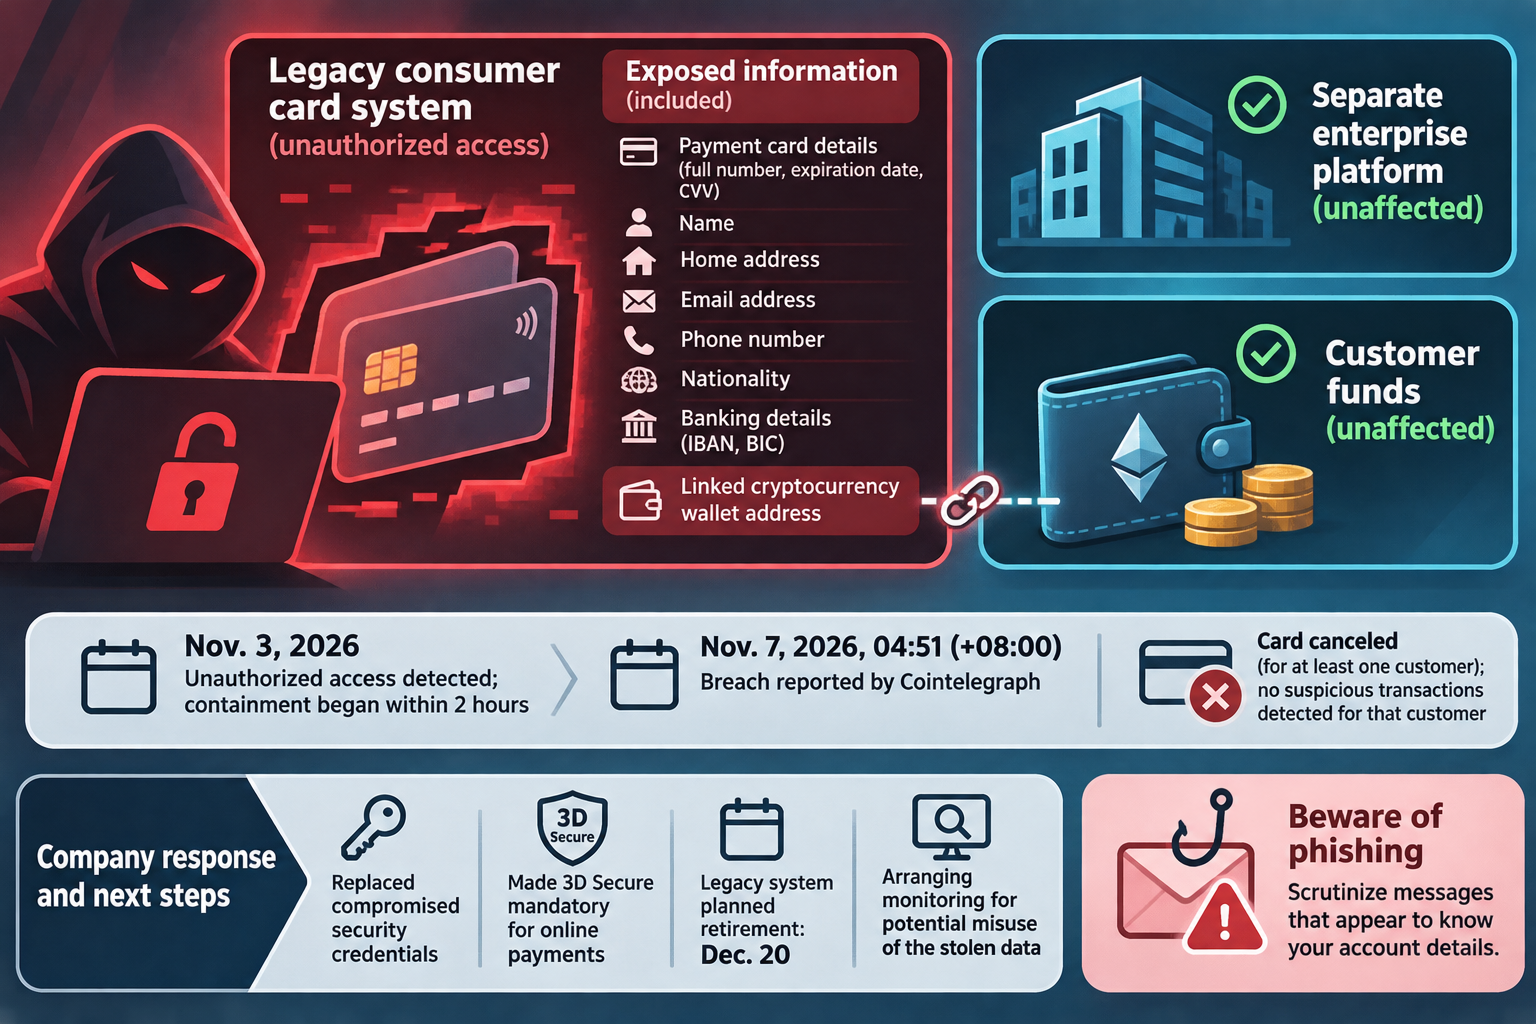
The company said it replaced compromised security credentials, addressed the vulnerability and made 3D Secure verification mandatory for online payments until the legacy system’s planned retirement on Dec. 20. It also warned customers about phishing attempts that could use their personal or transaction details and said it was arranging monitoring for potential misuse of the stolen data. For affected cardholders, that warning is a reason to scrutinize messages that appear to know account details rather than treat such details as proof that a message is genuine.
Source: cointelegraph.com (originally published 2026-11-07 04:51 UTC+8)