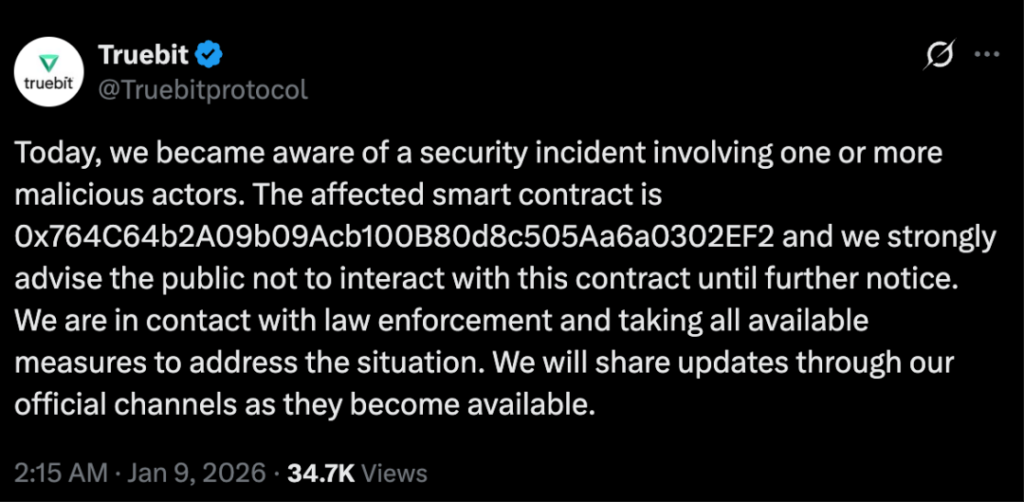
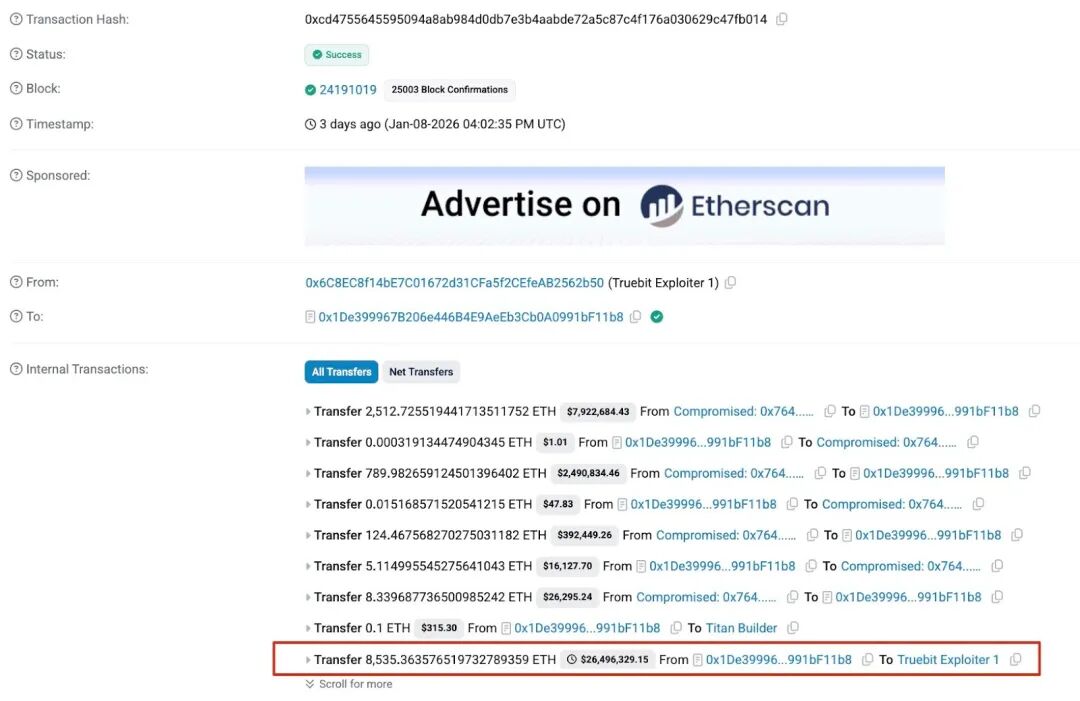
A contract that manages a token’s ETH reserves depends on its pricing calculation being correct. In an analysis published on January 12, 2026, SlowMist said an attacker exploited an arithmetic overflow in Truebit Protocol’s Purchase contract on January 8, allowing TRU tokens to be minted for zero ETH and redeemed against the contract’s reserves. SlowMist’s MistTrack estimated the attacker’s proceeds at approximately 8,535 ETH, worth about $26.44 million at the time of its analysis.
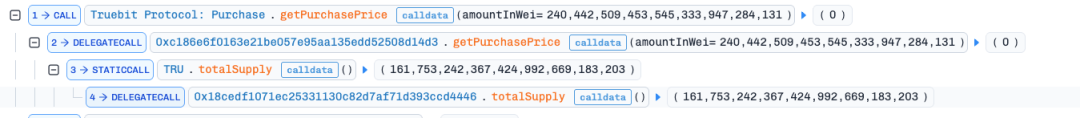
What failed in the price calculation
Truebit’s Purchase contract calculated how much ETH a user had to pay to mint a requested amount of TRU. According to SlowMist’s analysis of the contract, multiplication in the pricing calculation used SafeMath overflow checks, but an addition in the numerator used the native + operator without such protection.
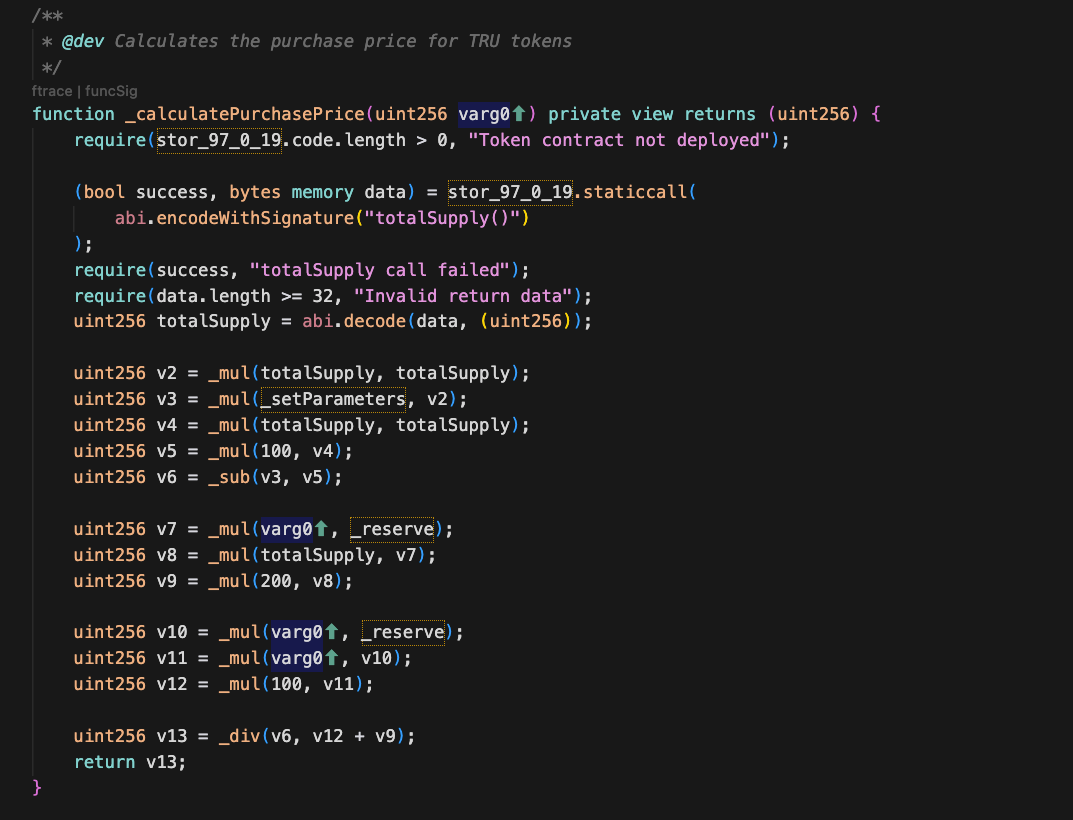
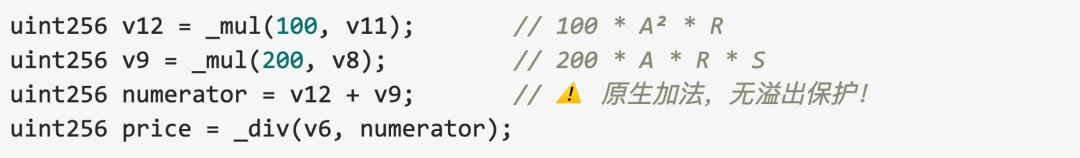
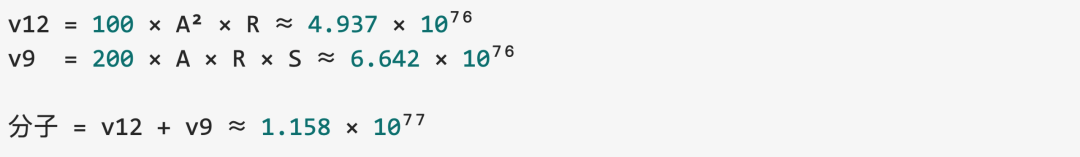
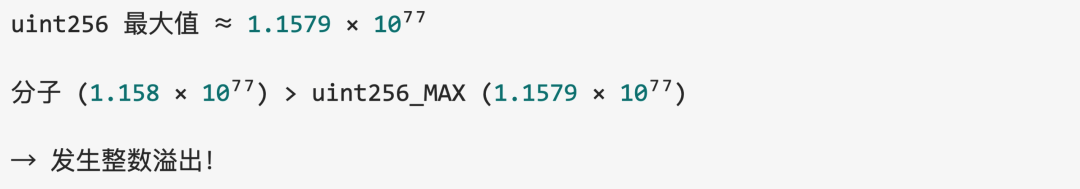
The contract was compiled with Solidity 0.6.10, a version in which native arithmetic did not automatically check for overflow. SlowMist said the attacker chose a mint amount that let the checked multiplications succeed while causing the unchecked addition to exceed the maximum uint256 value. The result wrapped around to a small number; subsequent integer division returned a mint price of zero ETH.
How the reserves were withdrawn
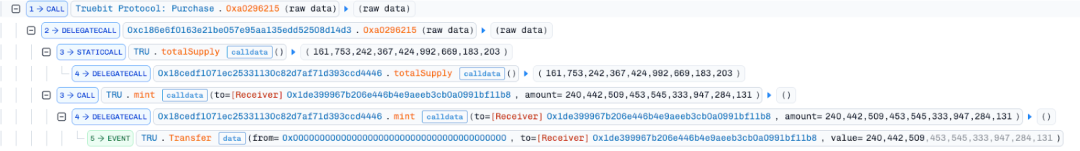
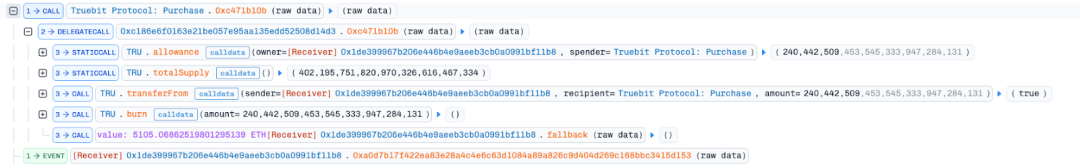
SlowMist identified an initial request to mint 240,442,509,453,545,333,947,284,131 TRU. It said the attacker minted that amount without paying ETH, then burned the tokens to withdraw 5,105.069 ETH from the Purchase contract’s reserves. The attacker repeated the mint-and-burn process. Later mints required some ETH as the token supply changed, but SlowMist said the attacker continued until the contract’s ETH reserves were exhausted.
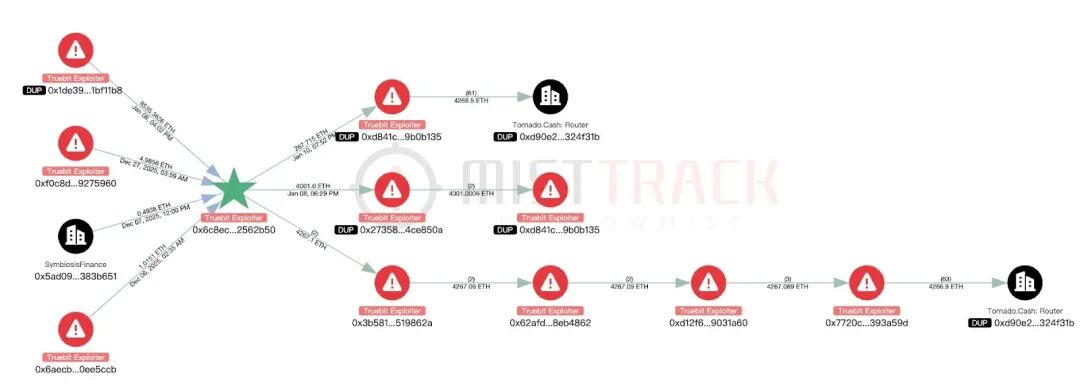
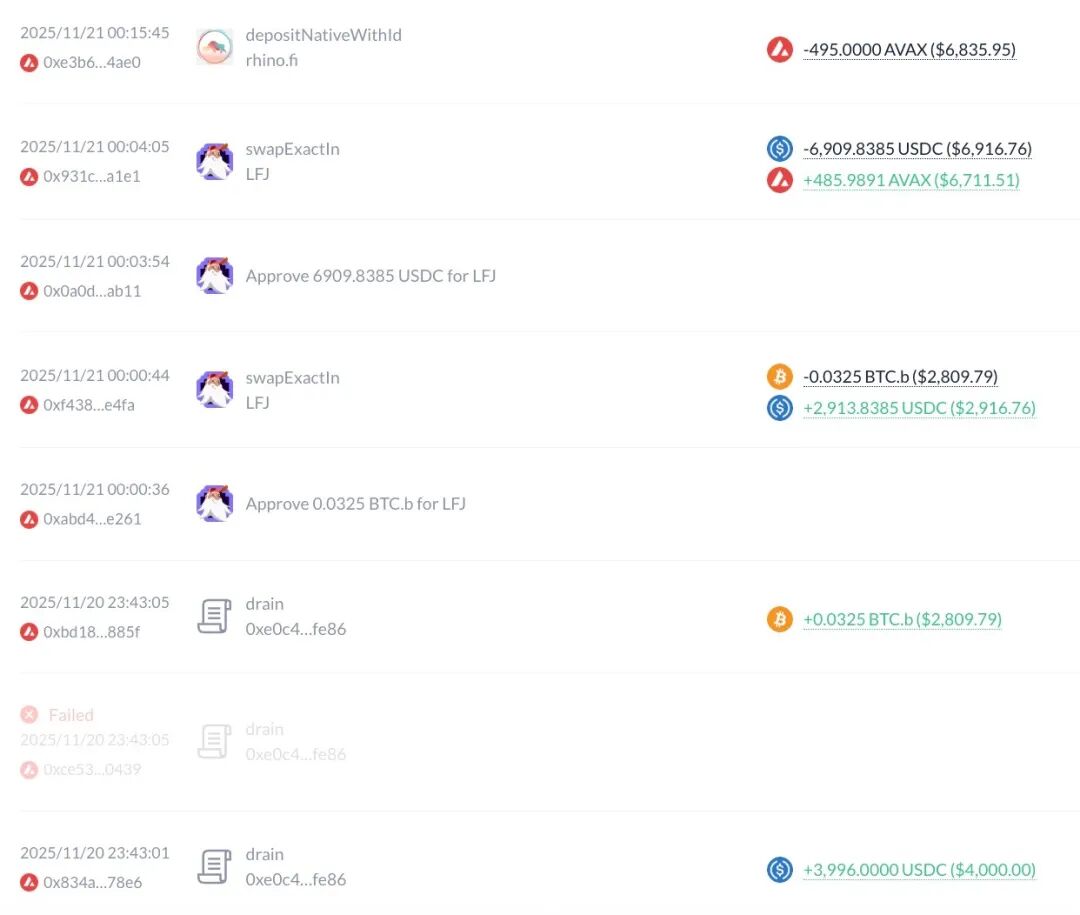
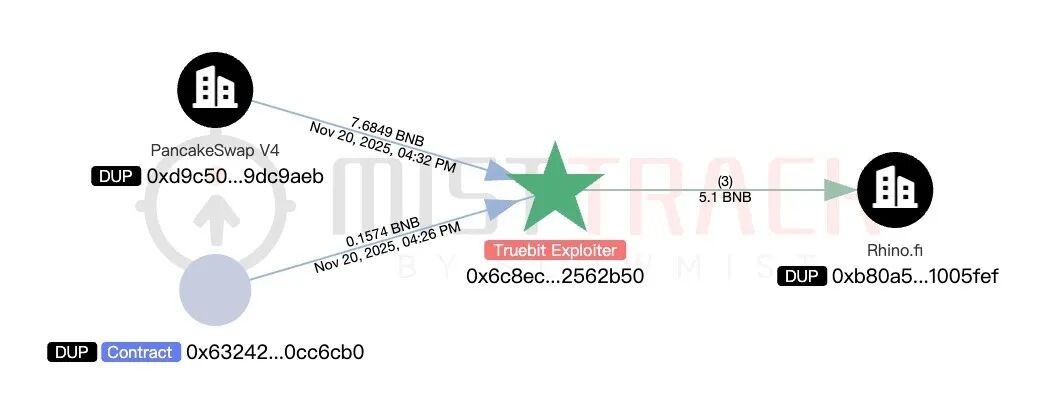
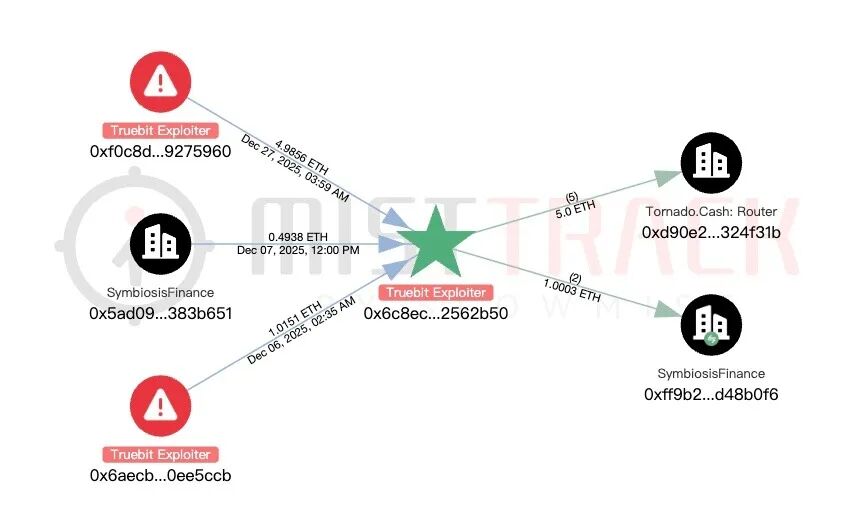
MistTrack reported that approximately 8,535 ETH from the incident went first to three new addresses and ultimately to Tornado Cash. Those proceeds and their route are SlowMist’s tracking findings, not independently established figures here.
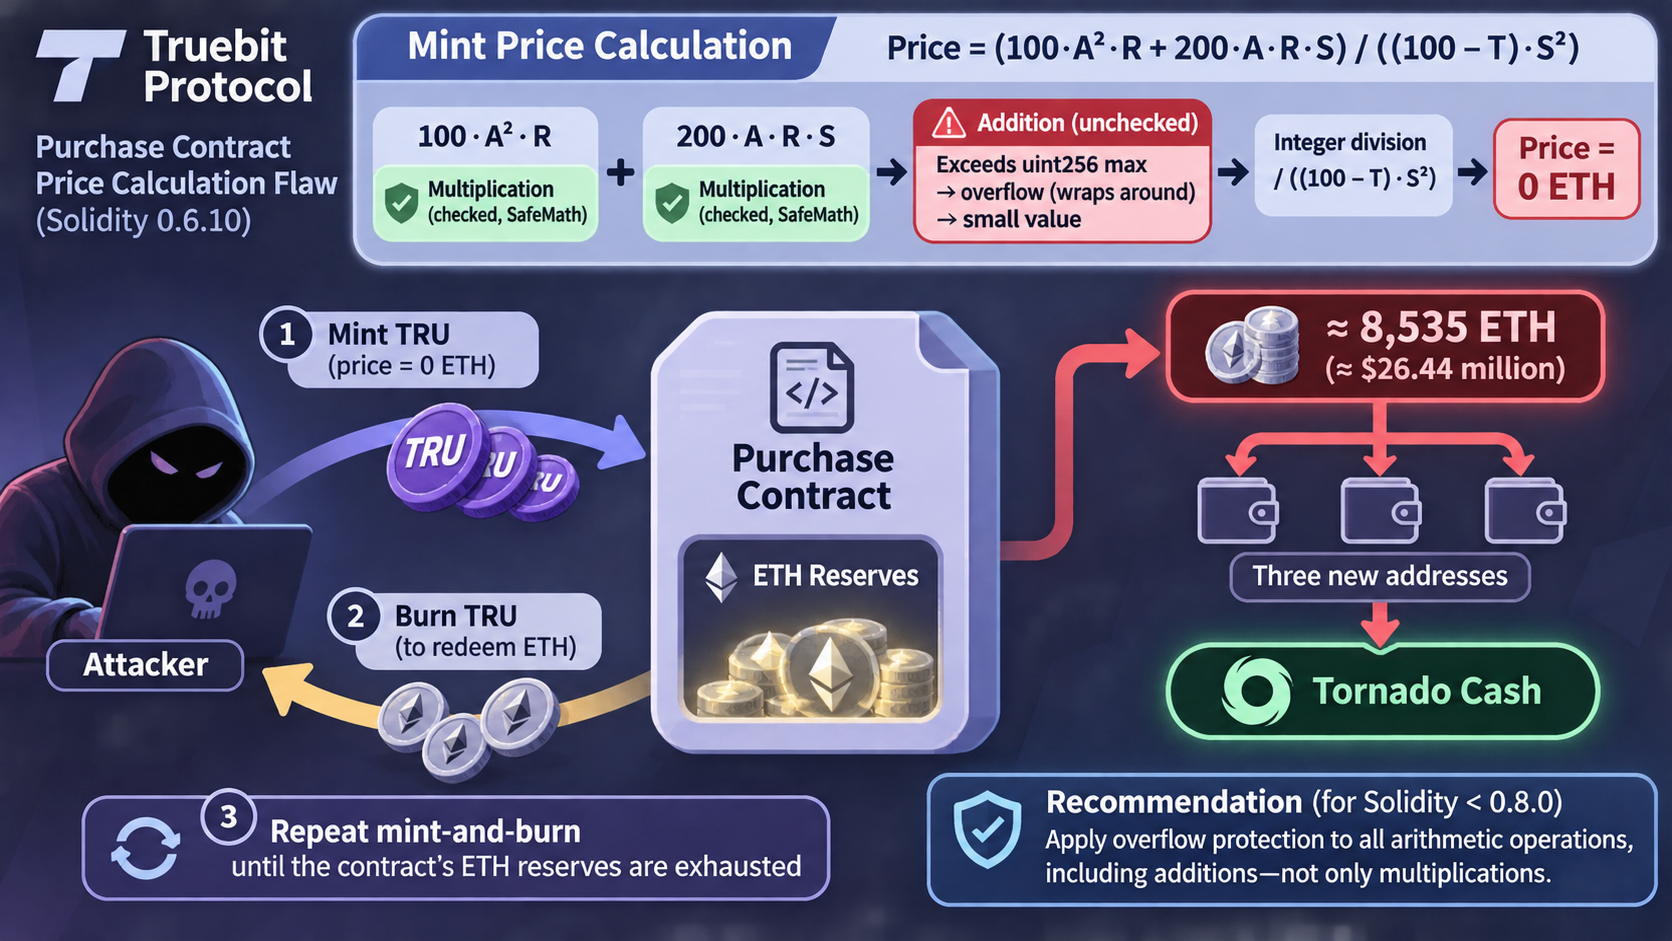
The failure was in the contract’s pricing logic, not a reported compromise of users’ wallet recovery information. SlowMist’s recommendation for developers using Solidity versions before 0.8.0 was to apply overflow protection to all arithmetic operations, including additions—not only multiplications.