If you keep bitcoin on a Lightning wallet you run yourself, the practical question after a reported theft is not only whether a newer version exists. It is whether keys and other secrets already on that server should still be treated as confidential.
In a report published on November 11, 2026, Cointelegraph said Bitcoin Lightning wallet platform LNbits had urged users to update immediately after a wave of attacks on LNbits instances that resulted in stolen funds. The project published version 1.7.0 on Tuesday and described it as a critical release addressing vulnerabilities and strengthening authentication, extension management, and payment handling. LNbits warned that updating alone would not protect installations whose credentials had already been compromised.
LNbits creator Ben Arc said on X: “It’s been a very challenging few days, working relentlessly to get the v1.7 release out after our users and we suffered losses.” The report did not give a figure for those losses. Cointelegraph said it had reached out to Ben Arc and LNbits for comment.
LNbits provides software for running Bitcoin Lightning wallets and payment applications, including merchant checkouts, tipping services, and paywalls. Ben Arc said in May that about 200,000 people run the software themselves. That was his May statement about self-hosting, not a count of how many instances this incident affected.
As the November 11 report described the sequence, LNbits first warned operators on Sunday to disable the Paywall extension while it investigated a potential vulnerability. Just over an hour later, it urged users to shut down their LNbits servers immediately, citing a wave of attacks, and it took its own hosted installations offline. LNbits had not yet detailed the exploit or how many people were affected. It said a separate report on the exploit would follow.
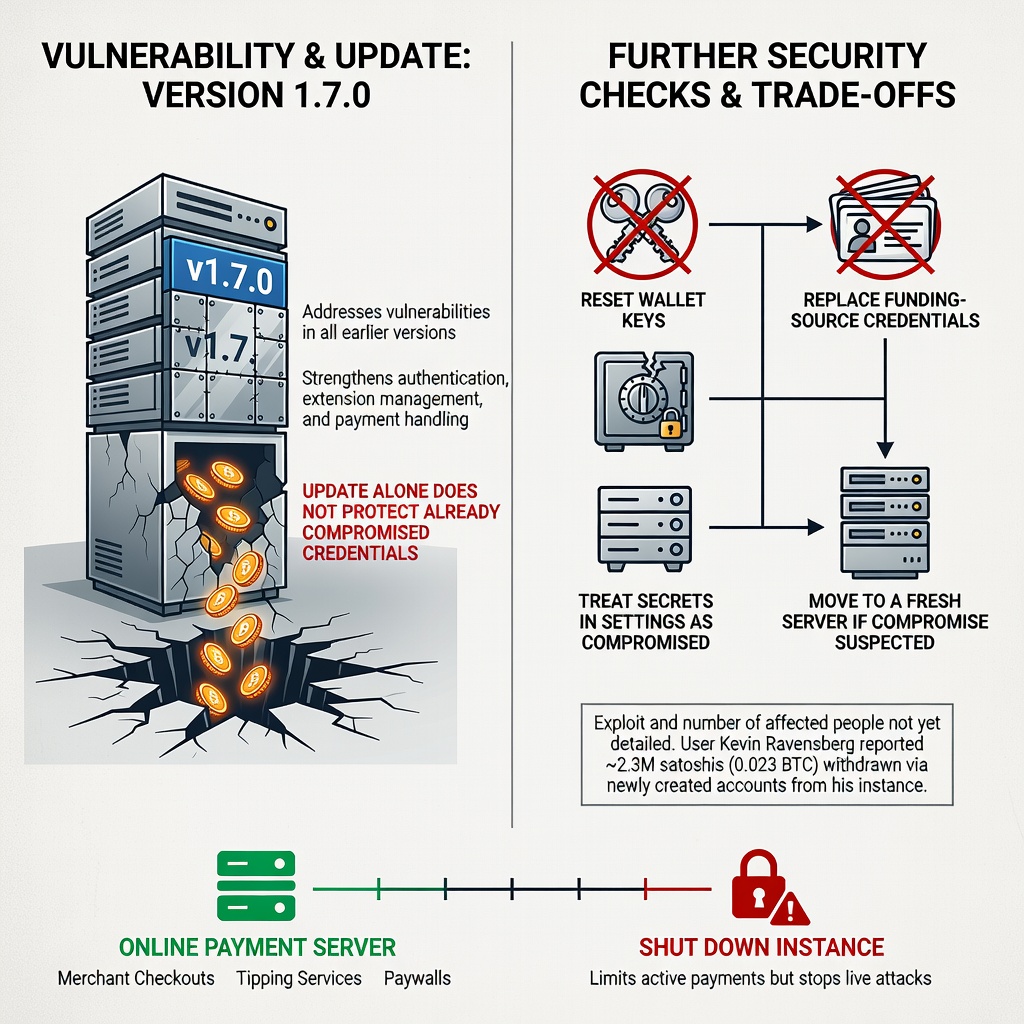
In the announcement with the emergency patch, LNbits said the vulnerability affects all versions before 1.7.0 and puts funds at risk of theft. It also warned that credentials exposed before an upgrade could still give attackers access afterward. Operators were urged to reset wallet keys, replace funding-source credentials, and treat secrets stored in LNbits settings as compromised. If a compromise was suspected, LNbits recommended moving to a fresh server.
One user, Kevin Ravensberg, said attackers exploited his LNbits instance and withdrew about 2.3 million satoshis, or 0.023 bitcoin, through newly created accounts before he could shut the server down. That is his account of his own instance. It is not a confirmed total for the wider incident, and the project had not published how many people were affected.
The trade-off in the project’s own advice was between keeping a payment server reachable and stopping a live attack. Shutting an instance down limits checkouts, tips, and other payments that depend on it. Installing 1.7.0 changes the software boundary for versions before that release, but LNbits said it does not protect secrets that were already exposed. Resetting wallet keys, replacing funding-source credentials, treating settings secrets as compromised, and moving to a fresh server when compromise is suspected are separate from the update. None of those steps recovers funds already reported stolen, and none of them removes every risk of operating a wallet server.
Source: cointelegraph.com (originally published 2026-11-11 09:16 UTC+8)